Cisco Networking and CCNA Concepts
Study these flashcardsFree · spaced repetition · iPhone, Android, Mac & web
All cards
1
Which of the following OSPF network types have a default hello timer of 10 seconds and a default dead timer of 40 seconds? (Select 2 choices.)
- broadcast
- point-to-multipoint
- point-to-point
- nonbroadcast
- point-to-multipoint nonbroadcast
2
You want to configure an interface on your Cisco router to receive a dynamic IP address from a DHCP server on your network. The IP addresses should be assigned from the 192.168.1.0/26 address range.
Which of the following commands should you issue?
Which of the following commands should you issue?
- network 192.168.1.0 255.255.255.192
- host 192.168.1.0 255.255.255.192
- ip dhcp pool 1
- ip address dhcp
3
Which of the following is enabled on a Cisco router when you issue the ntp server command from global configuration mode? (Select the best answer.)
- authentication
- server mode
- symmetric active mode
- static client mode
- symmetric active mode
4
Which of the following can be implemented to provide assisted roaming in a wireless network?
- 802.11v
- 802.11k
- 802.11r
- 802.11w
5
Which of the following best describes an AP deployment that connects APs to a WLC that is housed within a switch stack? (Select the best answer.)
- cloud-based AP deployment
- embedded AP deployment
- autonomous AP deployment
- lightweight AP deployment
6
7
Which of the following WLC interfaces is typically used for continuous SNMP polling? (Select the best answer.)
- a dynamic interface
- the AP-manager interface
- the virtual interface
- the service port interface
- the management interface
8
Which of the following statements about unique local unicast IPv6 addresses are true? (Select 2)
- The first 7 bits of the prefix are always 1111110
- They are assigned by ICANN
- They are unique only within an organization
- They can communicate only over a single link
- They are assigned by ICANN
9
Which of the following IPv6 prefixes is used for multicast addresses?
- 2000::/3
- FE80::/10
- FF00::/8
- FD00::/8
- FC00::/8
10
HostA sends a packet that is destined for HostB. When will the router check access list 10?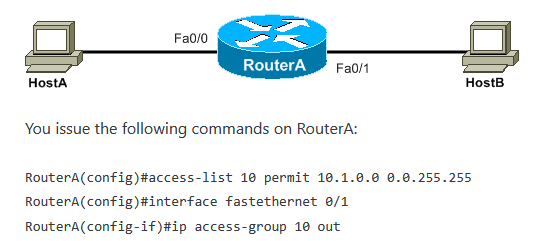
- RouterA will check access list 10 before the packet enters interface Fa0/0
- RouterA will check access list 10 after the packet is routed to interface FastEthernet 0/1.
- RouterA will check access list 10 after the packet enters interface Fa0/0 and again after the packet is routed to interface Fa0/1
- RouterA will check access list 10 after the packet enters interface Fa0/0 but before the packet is routed to interface Fa0/1
- RouterA will not check access list 10 for this packet
11
You administer the network shown in the exhibit. You have created an inspection rule named boson and applied the inspection rule to the untrusted interface in the outbound direction.
You want to protect the internal network from external threats while allowing legitimate IP traffic from the internal network to communicate with the external network.
Which of the following command sets should you issue?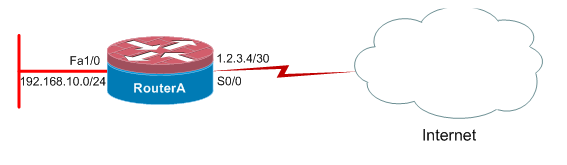
You want to protect the internal network from external threats while allowing legitimate IP traffic from the internal network to communicate with the external network.
Which of the following command sets should you issue?
- access-list 101 deny ip 1.2.3.4 0.0.0.3 any / access-list 101 deny ip host 255.255.255.255 any / access-list 101 permit ip any any / interface s0/0 / ip access-group 101 in
- access-list 102 deny ip 192.168.10.0 0.0.0.255 any log / access-list 102 permit icmp any host 1.2.3.5 unreachable / access-list 102 deny ip any any / interface s0/0 / ip access-group 102 in
- access-list 102 deny ip 192.168.10.0 0.0.0.255 any log / access-list 102 permit icmp any host 1.2.3.5 unreachable / access-list 102 deny ip any any / interface fa1/0 / ip access-group 102 in
- access-list 101 deny ip 1.2.3.4 0.0.0.3 any / access-list 101 deny ip host 255.255.255.255 any / access-list 101 permit ip any any / interface fa1/0 / ip access-group 101 out
12
Which of the following commands could you use to disable authentication for vty, console, or AUX connections to a router? (Select the best answer.)
- aaa authentication login none local
- aaa authentication login local none
- aaa authentication login default local
- aaa authentication login disable none
13
Which of the following is centralized on an SDN network?
- the application plane
- the data plane
- the management plane
- the control plane
14
You want to configure SSH for incoming vty connections on a new router. The router is running a K9 IOS image but has not yet been configured with a host name, a domain name, or an RSA key pair. In addition, the vty lines are not yet configured to accept incoming SSH connections.
You issue the crypto key generate rsa command from global configuration mode.
Which of the following messages will you most likely receive?
You issue the crypto key generate rsa command from global configuration mode.
Which of the following messages will you most likely receive?
- Please define a hostname other than Router
- The name for the keys will be:
- Please create RSA keys to enable SSH
- Please enable SSH as a transport mode
- Please define a domain-name first
15
Which of the following connects a wireless client to a wired network without requiring a separate wireless controller?
- embedded AP deployment
- cloud-based AP deployment
- lightweight AP deployment
- autonomous AP deployment
16
Rapid PVST+ is a Cisco enhancement of which of the following IEEE protocols? (Select the best answer.)
- 802.1Q
- 802.1t
- 802.1w
- 802.1s
- 802.1D
17
Which of the following WLC interfaces controls all Layer 3 communications between a WLC and a lightweight AP?
- the virtual interface
- the management interface
- a dynamic interface
- the service port interface
- the AP-manager interface
18
Which of the following IPv6 address prefixes are not routable? (select two)
- FF02::/16
- FC00::/8
- 2000::/3
- FF05::/16
- FE80::/10
- FD00::/8
19
You have been asked to summarize your network addresses into a single summarized subnet. The addresses on your network consist of the following addresses:
10.1.1.64/27
10.1.1.96/27
10.1.1.128/27
10.1.1.160/27
In order to preserve address space, you should summarize these networks by using the most efficient subnet mask
10.1.1.64/27
10.1.1.96/27
10.1.1.128/27
10.1.1.160/27
In order to preserve address space, you should summarize these networks by using the most efficient subnet mask
- /26
- /24
- /25
- /23
20
You have been asked to summarize your network addresses into a single summarized subnet. The addresses on your network consist of the following addresses:
10.1.1.128/27
10.1.1.160/27
10.1.1.192/27
10.1.1.224/27
In order to preserve address space, you should summarize these networks by using the most efficient subnet mask.
10.1.1.128/27
10.1.1.160/27
10.1.1.192/27
10.1.1.224/27
In order to preserve address space, you should summarize these networks by using the most efficient subnet mask.
- /24
- /25
- /23
- /26
21
Which of the following are used by WPA2 to provide MICs and encryption? (Select 2 choices.)
- RC4
- AES
- CCMP
- GCMP
- TKIP
22
You are configuring Layer 2 security on a WLAN by using the WLC GUI. You select WPA+WPA2 from the Layer 2 Security drop-down list box. You want to configure the WPA2 key in hexadecimal format.
Which of the following WPA2 key management methods should you select from the Auth Key Mgmt drop-down list box?
Which of the following WPA2 key management methods should you select from the Auth Key Mgmt drop-down list box?
- 802.1X
- PSK
- 802.1X+CCKM
- CCKM
23
You issue the show vlan brief command on Switch1 and receive the following partial output:
You issue the following commands on Switch1:
Which of the following statements is true? (Select the best answer.)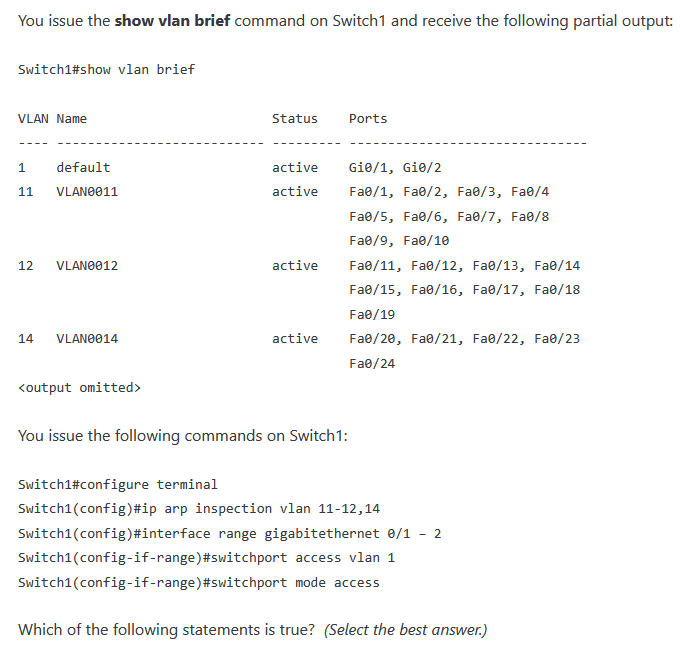
You issue the following commands on Switch1:
Which of the following statements is true? (Select the best answer.)
- Only GigabitEthernet 0/1 and GigabitEthernet 0/2 ports are untrusted ports
- Only GigabitEthernet 0/1 and GigabitEthernet 0/2 are trusted ports.
- DAI is configured on only GigabitEthernet 0/1 and GigabitEthernet 0/2.
- DAI is not configured on GigabitEthernet 0/1 and GigabitEthernet 0/2
24
You are implementing common Layer 2 security measures on a Cisco switch. You create a new VLAN with an ID of 4. No devices operate on VLAN 4. You issue the following commands on a switch interface:
switchport access vlan 4
switchport mode access
Which of the following Layer 2 security measures are you implementing? (Select 2 choices.)
switchport access vlan 4
switchport mode access
Which of the following Layer 2 security measures are you implementing? (Select 2 choices.)
- enabling port security on an access port
- moving the port to an unused VLAN
- disabling DTP on a port completely
- disabling an unused port
- configuring the port mode manually
25
Your company has added an email server and a web server to the existing network infrastructure. Company policy stipulates that only inbound SMTP traffic be allowed to pass to Email Server and that only inbound web traffic be allowed to pass to Web Server. All other traffic must be prevented from reaching the subnet.
Which access lists should be applied to the S0/0 interface of Router1? (Select 2)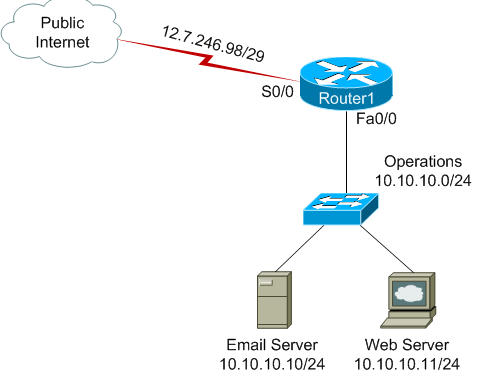
Which access lists should be applied to the S0/0 interface of Router1? (Select 2)
- access-list 101 permit tcp any 10.10.10.10 0.0.0.0 eq 25
- access-list 101 permit tcp any 10.10.10.10 0.0.0.255 eq 25
- access-list 101 permit udp any 10.10.10.11 0.0.0.0 eq 80
- access-list 101 permit udp any 10.10.10.10 0.0.0.0 eq 25
- access-list 101 permit tcp any 10.10.10.11 0.0.0.255 eq 80
- access-list 101 permit tcp any 10.10.10.11 0.0.0.0 eq 80
26
The sending device on a site-to-site VPN that is constructed by using GRE with IPSec for transport encrypts a new packet.
Which of the following steps occurs next? (Select the best answer.)
Which of the following steps occurs next? (Select the best answer.)
- The sending device adds a VPN header and an IP header.
- The sending device sends the packet to the destination.
- The sending device adds the session key to the packet.
- The receiving device decrypts the packet.
27
The sending device on a site-to-site VPN that is constructed by using GRE with IPSec for transport encrypts a new packet.
- The sending device adds a VPN header and an IP header.
- The receiving device decrypts the packet.
- The sending device adds the session key to the packet.
- The sending device sends the packet to the destination.
28
Which of the following entries from the show ip route command indicates a host route?
- C 192.168.1.0/30 is directly connected, FastEthernet0/0
- O 192.168.1.0/24 [110/2] via 10.1.1.13, 00:00:08, FastEthernet0/0
- L 192.168.1.1/32 is directly connected, FastEthernet0/0
- S 192.168.1.0/24 [5/0] via 10.1.2.3
- S* 0.0.0.0/0 [1/0] via FastEthernet0/0
29
You issue the show ip route command on RouterA and receive the following partial output:
S 10.20.0.0/22 [1/0] via 192.168.10.2
R 10.20.0.0/24 [120/3] via 192.168.10.3, 00:33:38, Serial0/3
D 10.20.0.0/26 [90/2809856] via 192.168.10.4, 00:02:14, Serial0/4
O 10.20.0.0/28 [110/64] via 192.168.10.1, 00:02:38, Serial0/1
RouterA receives a packet that is destined for 10.20.0.14.
Which of the following routes will RouterA use to send the packet? (Select the best answer.)
- the OSPF route, because it is the route with the longest prefix match
- the EIGRP route, because it has the lowest AD
- the static route, because static routes are preferred over dynamic routes
- the RIP route, because it has the highest AD
30
You have connected the GigabitEthernet 0/1 interface of RouterC to RouterB and configured the appropriate interface addresses on both routers.
Which of the following commands could you issue on RouterC to enable communication between RouterC and RouterA? (Select all that apply.)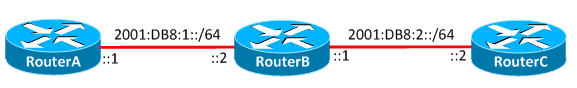
Which of the following commands could you issue on RouterC to enable communication between RouterC and RouterA? (Select all that apply.)
- ipv6 route 2001:DB8:1::2 2001:DB8:2::/64
- ipv6 route ::/0 GigabitEthernet 0/1
- ipv6 route 2001:DB8:2::/64 2001:DB8:1::2
- ipv6 route 2001:DB8:1::/64 2001:DB8:2::1
- ipv6 route 2001:DB8:2::1 2001:DB8:1::/64
31
You issue the following commands on a Cisco router's FastEthernet 0/0 interface:
ipv6 address 2001:DB8:A::/64 eui-64
no shutdown
The interface on the other side of the link is not yet configured. In addition, there is no DHCPv6 server on the network.
ipv6 address 2001:DB8:A::/64 eui-64
no shutdown
The interface on the other side of the link is not yet configured. In addition, there is no DHCPv6 server on the network.
- three
- two
- none
- one
32
Which of the following statements is true regarding the ip access-group command?
- It can be used to apply an ACL to an IPv4 interface
- It can be used to apply an IPv4 ACL to a vty line
- It can be used to apply an ACL to an IPv6 interface
- It can be used to apply an IPv6 ACL to the AUX line
33
Which wireless security protocol relies on SAE and introduces support for PMF?
- WPA3-Enterprise
- WPA2-Personal
- WPA3-Personal
- WPA2-Enterprise
34
Which of the following commands should you issue in order to encrypt the password that is required to access privilege level 7 on a router?
- enable password level 7 cisco
- enable secret 7 cisco
- enable password 7 cisco
- enable secret level 7 cisco
35
You are configuring Layer 2 security on a WLAN by using the WLC GUI. You select WPA+WPA2 from the Layer 2 Security drop-down list box. You then select the MAC Filtering option to ensure that only specific clients can join, and you select the WPA2 Policy option to ensure that WPA2 is used. You want to minimize the amount of time it takes an 802.1X client to roam between APs.
Which of the following WPA2 key management methods should you select from the Auth Key Mgmt drop-down list box?
Which of the following WPA2 key management methods should you select from the Auth Key Mgmt drop-down list box?
- 802.1X+CCKM
- 802.1X
- CCKM
- PSK
36
Which of the following statements are true about IPSec configured in tunnel mode? (Select 2)
- It encrypts both the IP header and the payload
- It is less secure than IPSec configured in transport mode
- It encrypts the IP header but does not encrypt the payload
- It is often used in networks with private IP addresses
- It encrypts the payload but does not encrypt the IP header
37
You issue the following commands on Switch1:
Switch1(config)#ip arp inspection vlan 11,14,18
Switch1(config)#interface fastethernet 0/1
Switch1(config-if)#switchport access vlan 14
Switch1(config-if)#switchport mode access
Switch1(config-if)#ip arp inspection trust
Switch1(config-if)#interface range fastethernet 0/2 - 4
Switch1(config-if-range)#switchport access vlan 14
Switch1(config-if-range)#switchport mode access
Which of the following statements are true? (Select 2 choices.)
- Ports in every VLAN except VLAN 14 are trusted ports
- Every port except the FastEthernet 0/1 port in VLAN 14 is an untrusted port
- Every port in VLANs 11, 14, and 18 is an untrusted port
- The FastEthernet 0/1 port in VLAN 14 is a trusted port
- All ports in VLAN 14 are trusted ports
38
You issue the following command on a Cisco router in global configuration mode:
ipv6 route 2001:db8:a::/32 fastethernet 0/1
Which of the following have you created?
ipv6 route 2001:db8:a::/32 fastethernet 0/1
Which of the following have you created?
- a recursive static route
- a directly attached static route
- a fully specified static route
- a floating static route
39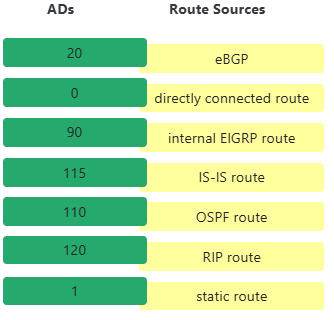
Select the following ADs, and drag them to their corresponding route sources. 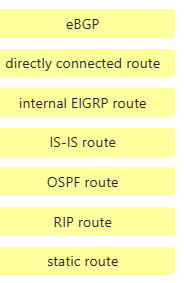
40
You issue the ip ospf network non-broadcast command on an interface.
Which of the following statements is correct regarding how OSPF operates on the interface? (Select the best answer.)
Which of the following statements is correct regarding how OSPF operates on the interface? (Select the best answer.)
- The hello timer is set to 10 seconds, and the dead timer is set to 40 seconds.
- DR and BDR elections are not performed.
- The neighbor command is required to establish adjacencies.
- Multicast updates are sent.
41
How is the OSPF DR for a multiaccess network segment determined?
- first by the highest OSPF priority value, then by the highest configured router ID, then by the highest loopback IP address, and then by the highest physical IP address
- first by the highest OSPF priority value, then by the highest router ID, and then by the highest IP address
- first by the highest configured router ID, then by the highest OSPF priority value, then by the highest loopback IP address, and then by the highest physical MAC address
- first by the highest OSPF priority value, then by the highest loopback IP address, and then by the highest physical IP address
- first by the highest router ID, then by the highest loopback IP address, and then by the highest physical IP address
- first by the highest router ID, then by the highest loopback IP address, and then by the highest physical MAC address
42
Your supervisor wants you to reduce the range of IP addresses available from a NAT pool that is configured on the department router. You should do this by enabling internal hosts to share a single external IP address.
Which of the following should you configure on RouterA?
Which of the following should you configure on RouterA?
- NAT overlapping
- dynamic NAT
- static NAT
- NAT overloading
43
Which of the following can be implemented to help protect against spoofed management frames in a wireless network?
- 802.11w
- 802.11r
- 802.11k
- 802.11v
44
Which of the following statements is accurate regarding alternate ports?
- An alternate port is the port on a switch that has the best path to the root bridge
- An alternate port is a blocked port that receives more useful BPDUs from a port on another switch
- An alternate port is always in the forwarding state
- An alternate port is the port on a segment that has the best path to the root bridge
- An alternate port is a blocked port that receives more useful BPDUs from another port on the local switch
45
Which of the following subnet addresses is most appropriate for the point-to-point link between RouterA and RouterB?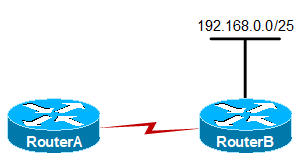
- 192.168.0.0/25
- 192.168.0.128/25
- 192.168.0.0/30
- 192.168.0.128/30
- 192.168.0.192/26
- 192.168.0.130/30
46
Which of the following digital networking technologies has a total bandwidth of 1.544 Mbps? (Select the best answer.)
- E3
- T3
- E1
- T1
47
Which of the following are used by WPA2 to provide MICs and encryption? (Select 2 choices.)
- GCMP
- AES
- CCMP
- TKIP
- RC4
48
You administer the network shown above. You want to configure RouterA so that only RouterB can Telnet to RouterA. No other traffic to or from RouterA should be affected.
Which of the following commands should you issue to complete this task? (Select all that apply.)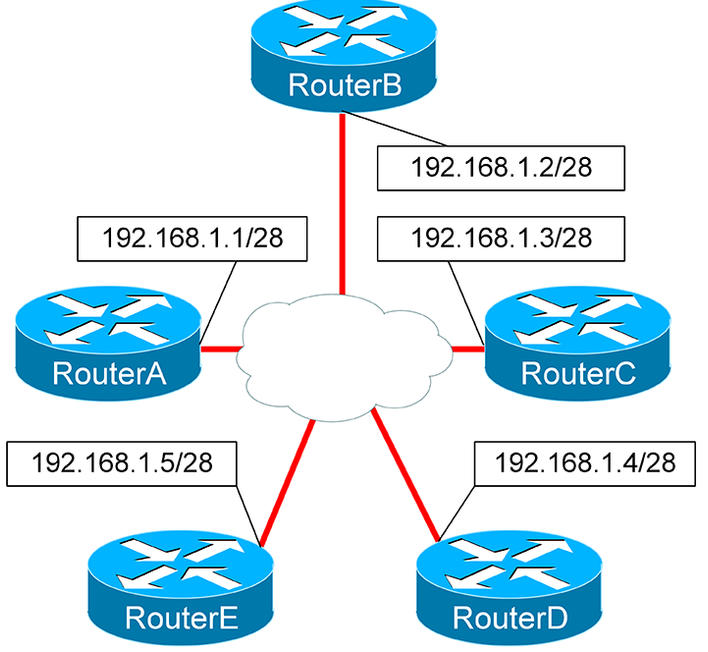
Which of the following commands should you issue to complete this task? (Select all that apply.)
- ip access-group 10 in
- ip access-group 10 out
- access-class 10 in
- access-list 10 permit 192.168.1.2 0.0.0.0
- access-list 10 permit 192.168.1.2 0.0.0.15
- access-class 10 out
49
Which of the following technologies is implemented in WPA3-Enterprise to improve authentication encryption?
- PMF
- ECDSA
- SAE
- AES-GCMP
50
You want to configure your Cisco router to provide IP addresses to the computers on your network. The IP addresses should be assigned from the 192.168.1.0/26 address range.
Which of the following commands should you issue? (select 2)
Which of the following commands should you issue? (select 2)
- dhcp pool 1
- ip dhcp pool 1
- host 192.168.1.0 255.255.255.192
- network 192.168.1.0 255.255.255.192
- ip address dhcp
- network 192.168.1.0 0.0.0.63
51
You are migrating your company's IPv4 network to IPv6. The company has decided to use the 2001:DB8:A::/120 subnet throughout the network. You have been asked to configure RouterA and RouterB with IPv6 addresses on each end of the point-to-point link. RouterA should be assigned the next-to-last host address in the company's address range, and RouterB should be assigned the last host address. In order to conserve address space, you have been asked to use the /126 subnet
Which of the following commands should you issue to configure the interface on RouterB? (Select the best answer.)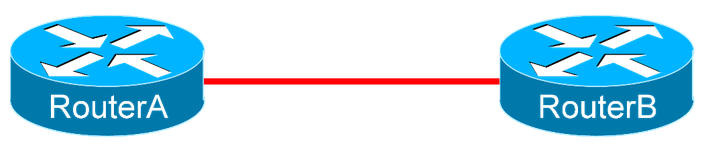
Which of the following commands should you issue to configure the interface on RouterB? (Select the best answer.)
- ipv6 address 2001:DB8:A::00FF/126
- ipv6 address 2001:DB8:A::00FE/126
- ipv6 address 2001:DB8:A::00FE/126
- ipv6 address 2001:DB8:A::FFFE/126
52
A REST API returns an HTTP status code of 301. Which of the following is the most likely reason this code was returned? (Select the best answer.)
- The requested resource cannot be found.
- The requested resource cannot be found.
- The requested action was successfully performed on the server.
- The requested resource has been permanently moved to another URL.
53
You issue the following commands on RouterA:
no service password-encryption
username admin password Z8O$0n!A\g Which of the following are true? (Select 2 choices.)
no service password-encryption
username admin password Z8O$0n!A\g Which of the following are true? (Select 2 choices.)
- The password will be stored with type 0 encryption
- The password has been issued with type 5 encryption
- The password has been issued with type 7 encryption
- The password has been issued with type 0 encryption.
- The password will be stored with type 7 encryption.
- The password will be stored with type 5 encryption.
54
Which of the following fields is not found in the header of a TCP packet?
- window
- acknowledgment number
- sequence number
- destination port
- length
- checksum
- source port
55
Which of the following commands enables a Cisco router to send DNS queries?
- ip dns server
- ip domain lookup
- ip host
- ip name-server
56
Which of the following does Terraform use as a modeling language?
- APIs
- SSH
- HCL
- YAML
57
Your supervisor informs you that several unauthorized employees in LAN A are downloading large files from FTP sites on the external network. Your supervisor has asked you to block all FTP access for LAN A. FTP access should be available to other users. The subnet corresponding to LAN A is 10.1.1.0/24.
Which of the following access list commands could you issue on RouterA to create an ACL that can be used to achieve your goal? (Select the best answer.)
Which of the following access list commands could you issue on RouterA to create an ACL that can be used to achieve your goal? (Select the best answer.)
- access-list 101 deny tcp 10.1.1.0 0.0.0.255 any eq 21
- access-list 1 deny tcp any 10.1.1.0 0.0.0.255 eq 21
- access-list 1 deny tcp 10.1.1.0 0.0.0.255 any eq ftp
- access-list 101 deny tcp any 10.1.1.0 0.0.0.255 eq ftp
58
You issue the following commands on a Cisco router named RouterA:
ip access-list extended boson
permit tcp any any range 22 443
deny tcp any any eq 23
permit tcp any any eq 20 21
permit tcp any any lt 442
permit tcp any any gt 444
Which of the following statements about the ACL is true?
ip access-list extended boson
permit tcp any any range 22 443
deny tcp any any eq 23
permit tcp any any eq 20 21
permit tcp any any lt 442
permit tcp any any gt 444
Which of the following statements about the ACL is true?
- Traffic that matches TCP destination ports in the range from 22 through 80 will be permitted
- Traffic that matches TCP destination port 23 will not be permitted.
- Traffic that matches TCP destination port 444 will be permitted.
- Traffic that matches TCP destination port 20 or TCP destination port 21 will be permitted.
59
You configure OSPF on a router and advertise all available interfaces. The serial interfaces are configured with PPP encapsulation and are using the default OSPF network type and timer values.
Which of the following statements is correct regarding how OSPF operates on the serial interfaces?
Which of the following statements is correct regarding how OSPF operates on the serial interfaces?
- Unicast updates are sent.
- DR and BDR elections are performed.
- The hello timer is set to 10 seconds, and the dead timer is set to 40 seconds.
- The neighbor command is required to establish adjacencies
60
Which of the following IPv6 addresses is a link-local multicast address that is used to send a packet to all routers on a segment?
- FF02::1
- FF05::2
- FF02::2
- FF05::1
61
Refer to the following command output from SwitchA:
SwitchA#show running-config | begin line
line con 0
line aux 0
line vty 0 4
login
password boson
line vty 5 15
login
password boson
!
no scheduler allocate
end
Which of the following is not true of SwitchA?
SwitchA#show running-config | begin line
line con 0
line aux 0
line vty 0 4
login
password boson
line vty 5 15
login
password boson
!
no scheduler allocate
end
Which of the following is not true of SwitchA?
- Remote login credentials will be sent to SwitchA as clear text.
- Users can access the device by using Telnet.
- Up to 16 remote users can simultaneously connect to SwitchA.
- The remote login password configured on the device is invalid.
62
You administer the network shown above. All the switches run RSTP.
Which of the following ports is an alternate port?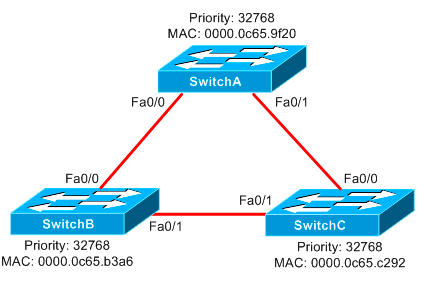
Which of the following ports is an alternate port?
- Fa0/1 on SwitchA
- Fa0/1 on SwitchC
- Fa0/0 on SwitchB
- Fa0/0 on SwitchA
- Fa0/0 on SwitchC
- Fa0/1 on SwitchB
63
You connect SwitchA and SwitchB as shown above. SwitchA is a Cisco switch, and SwitchB is a non-Cisco switch. You want to be able to trunk VLAN traffic between the two switches.
What commands should you issue on SwitchA? (Select 2 choices)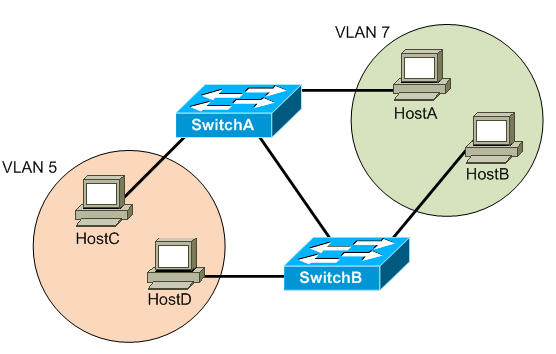
What commands should you issue on SwitchA? (Select 2 choices)
- SwitchA(config-if)# switchport mode trunk
- SwitchA(config-if)# switchport trunk encapsulation isl
- SwitchA(config)# switchport mode trunk
- SwitchA(config-if)# switchport mode access
- SwitchA(config)# switchport trunk encapsulation dot1q
- SwitchA(config-if)# switchport trunk encapsulation dot1q
64
You issue the following command on a Cisco router in global configuration mode:
ipv6 route 2001:db8:a::/32 fastethernet 0/1 2001:db8:b::1
Which of the following have you created? (Select the best answer.)
ipv6 route 2001:db8:a::/32 fastethernet 0/1 2001:db8:b::1
Which of the following have you created? (Select the best answer.)
- a fully specified static route
- a floating static route
- a floating static route
- a recursive static route
65
Which of the following refers to the process of buffering packets in a software queue on a QoS-enabled interface?
- queuing
- classification
- scheduling
- traffic policing
66
You issue the following command on your router:
RouterA#show cdp neighbors
Which of the following information will be displayed? (Select 4 choices.)
RouterA#show cdp neighbors
Which of the following information will be displayed? (Select 4 choices.)
- the interface on the neighboring device that is connected to RouterA
- the IP address of the neighboring device
- the interface on RouterA that is connected to the neighboring device
- the capabilities and product number of the neighboring device
- the software version running on the neighboring device
- the device ID of the neighboring device
67
Which of the following statements are true regarding dynamic interfaces on WLCs? (Select 2 choices.)
- Dynamic interfaces are user-defined.
- Dynamic interfaces are typically used for client data
- Dynamic interfaces are typically used for management information.
- Dynamic interfaces must be reachable by other WLCs
- Dynamic interfaces are often used for maintenance purposes.
68
Which of the following WLC interfaces is the only available interface when the WLC is booting?
- virtual interface
- dynamic interface
- management interface
- the service port interface
- AP-manager interface
69
Which of the following statements are true regarding a lightweight AP that is operating in FlexConnect mode? (Select 2)
- The lightweight AP can be used to detect rogue clients on a wired network.
- The lightweight AP can support client connections
- The lightweight AP can be remotely managed over a WAN link
- The lightweight AP must be connected to a WLC in order to operate
- The lightweight AP is running in the default lightweight AP mode
70
Which of the following prefixes will an IPv6-enabled computer use to automatically configure an IPv6 address for itself?
- FE80::/10
- 2000::/3
- FC00::/7
- FF00::/8
71
Which of the following pairs of IP addresses could you use at each end of a point-to-point link? (Select the best answer.)
- 10.1.1.62/30 and 10.1.1.65/30
- 10.1.1.127/30 and 10.1.1.128/30
- 10.1.1.2/30 and 10.1.1.3/30
- 10.1.1.236/30 and 10.1.1.237/30
- 10.1.1.153/30 and 10.1.1.154/30
72
Which of the following statements is true regarding link-local addresses? (Select the best answer.)
- They are used for ULA.
- They are not routable.
- They must never be used as destination addresses.
- They must never be used as source addresses.
- They must be globally unique
73
Which of the following commands can be issued to configure a Cisco router interface with the IPv6 address 2001:0000:0000:070D:0000:50A0:0001:0024 and a 96-bit subnet mask? (select 3)
- ipv6 address 2001::070d:0000:50a0:0001:0024/96
- ipv6 address 2001::070d::50a0:0001:0024/96
- ipv6 address 2001::070d:0:50a:0001:0024/96
- ipv6 address 2001:0:0:70d:0:50a0:1:24/96
- ipv6 address 2001::70d::50a:1:24/96
- ipv6 address 2001::70d:0:50a0:1:24/96
74
You are configuring Layer 2 security on a WLAN by using the WLC GUI. You select WPA+WPA2 from the Layer 2 Security drop-down list box. You then select the MAC Filtering option to ensure that only specific clients can join, and you select the WPA2 Policy option to ensure that WPA2 is used. You want to configure the WPA2 passphrase in ASCII format.
Which of the following WPA2 key management methods should you select from the Auth Key Mgmt drop-down list box? (Select the best answer.)
Which of the following WPA2 key management methods should you select from the Auth Key Mgmt drop-down list box? (Select the best answer.)
- PSK
- 802.1X+CCKM
- CCKM
- CCKM
75
Which of the following is true about IPSec configured in tunnel mode?
- It does not require an additional header
- It encrypts the entire packet.
- It is required for NAT traversal
- It does not encrypt the IP header.
More Computer science flashcards
Concepts of Programming LanguagesComputer science · EnglishLuluWindows Administration: Active Directory and AccountsComputer science · EnglishJaySection 1.1-1.3: Windows Commands/OSComputer science · Englishpzxlimemory Computer science · EnglisherikaCS 325 T7 L4,5,6Computer science · EnglishClementSecurity Plus PortsComputer science · EnglishJohnComputer Networks Part 2Computer science · EnglishSgPt. 1Computer science · EnglishCornyNa+- és vízháztartás zavaraiComputer science · HungarianRitikeAlgorithms itselfComputer science · EnglishSabs2023Microsoft Azure Administrator (AZ-104)Computer science · EnglishIsmaealITEC 110: Information Technology and CybersecurityComputer science · Englishmack
Study these decks in the app
Free on iPhone, Android, Mac and the web. Add any deck to your account in one tap.

