Missed Questions
Study these flashcardsFree · spaced repetition · iPhone, Android, Mac & web
All cards
1
Which of the following OSPF network types have a default hello timer of 10 seconds and a default dead timer of 40 seconds? (Select 2 choices.)
- nonbroadcast
- point-to-point
- broadcast
- point-to-multipoint
- point-to-multipoint nonbroadcast
2
You want to configure an interface on your Cisco router to receive a dynamic IP address from a DHCP server on your network. The IP addresses should be assigned from the 192.168.1.0/26 address range.
Which of the following commands should you issue?
Which of the following commands should you issue?
- host 192.168.1.0 255.255.255.192
- network 192.168.1.0 255.255.255.192
- ip dhcp pool 1
- ip address dhcp
3
Which of the following is enabled on a Cisco router when you issue the ntp server command from global configuration mode? (Select the best answer.)
- symmetric active mode
- symmetric active mode
- server mode
- static client mode
- authentication
4
Which of the following can be implemented to provide assisted roaming in a wireless network?
- 802.11v
- 802.11k
- 802.11r
- 802.11w
5
Which of the following best describes an AP deployment that connects APs to a WLC that is housed within a switch stack? (Select the best answer.)
- autonomous AP deployment
- embedded AP deployment
- lightweight AP deployment
- cloud-based AP deployment
6
Which of the following WLC interfaces is typically used for continuous SNMP polling? (Select the best answer.)
- the management interface
- a dynamic interface
- the AP-manager interface
- the service port interface
- the virtual interface
7
Which of the following statements about unique local unicast IPv6 addresses are true? (Select 2)
- They can communicate only over a single link
- They are assigned by ICANN
- The first 7 bits of the prefix are always 1111110
- They are unique only within an organization
- They are assigned by ICANN
8
Which of the following IPv6 prefixes is used for multicast addresses?
- 2000::/3
- FD00::/8
- FE80::/10
- FF00::/8
- FC00::/8
9
HostA sends a packet that is destined for HostB. When will the router check access list 10?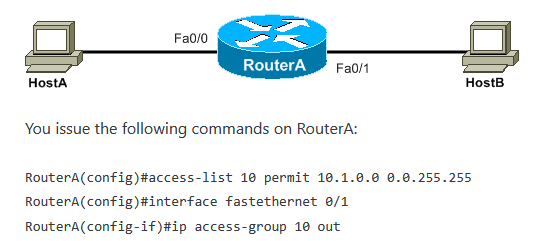
- RouterA will check access list 10 after the packet is routed to interface FastEthernet 0/1.
- RouterA will not check access list 10 for this packet
- RouterA will check access list 10 before the packet enters interface Fa0/0
- RouterA will check access list 10 after the packet enters interface Fa0/0 and again after the packet is routed to interface Fa0/1
- RouterA will check access list 10 after the packet enters interface Fa0/0 but before the packet is routed to interface Fa0/1
10
You administer the network shown in the exhibit. You have created an inspection rule named boson and applied the inspection rule to the untrusted interface in the outbound direction.
You want to protect the internal network from external threats while allowing legitimate IP traffic from the internal network to communicate with the external network.
Which of the following command sets should you issue?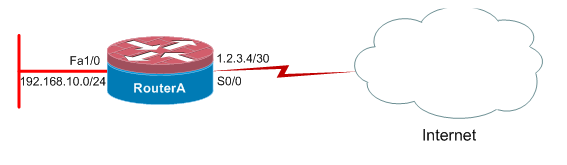
You want to protect the internal network from external threats while allowing legitimate IP traffic from the internal network to communicate with the external network.
Which of the following command sets should you issue?
- access-list 102 deny ip 192.168.10.0 0.0.0.255 any log / access-list 102 permit icmp any host 1.2.3.5 unreachable / access-list 102 deny ip any any / interface s0/0 / ip access-group 102 in
- access-list 101 deny ip 1.2.3.4 0.0.0.3 any / access-list 101 deny ip host 255.255.255.255 any / access-list 101 permit ip any any / interface s0/0 / ip access-group 101 in
- access-list 102 deny ip 192.168.10.0 0.0.0.255 any log / access-list 102 permit icmp any host 1.2.3.5 unreachable / access-list 102 deny ip any any / interface fa1/0 / ip access-group 102 in
- access-list 101 deny ip 1.2.3.4 0.0.0.3 any / access-list 101 deny ip host 255.255.255.255 any / access-list 101 permit ip any any / interface fa1/0 / ip access-group 101 out
11
Which of the following commands could you use to disable authentication for vty, console, or AUX connections to a router? (Select the best answer.)
- aaa authentication login default local
- aaa authentication login local none
- aaa authentication login none local
- aaa authentication login disable none
12
Which of the following is centralized on an SDN network?
- the control plane
- the management plane
- the data plane
- the application plane
13
You want to configure SSH for incoming vty connections on a new router. The router is running a K9 IOS image but has not yet been configured with a host name, a domain name, or an RSA key pair. In addition, the vty lines are not yet configured to accept incoming SSH connections.
You issue the crypto key generate rsa command from global configuration mode.
Which of the following messages will you most likely receive?
You issue the crypto key generate rsa command from global configuration mode.
Which of the following messages will you most likely receive?
- Please define a hostname other than Router
- Please create RSA keys to enable SSH
- Please define a domain-name first
- The name for the keys will be:
- Please enable SSH as a transport mode
14
Which of the following connects a wireless client to a wired network without requiring a separate wireless controller?
- autonomous AP deployment
- cloud-based AP deployment
- lightweight AP deployment
- embedded AP deployment
15
Rapid PVST+ is a Cisco enhancement of which of the following IEEE protocols? (Select the best answer.)
- 802.1w
- 802.1s
- 802.1t
- 802.1D
- 802.1Q
16
Which of the following WLC interfaces controls all Layer 3 communications between a WLC and a lightweight AP?
- the AP-manager interface
- the virtual interface
- the management interface
- the service port interface
- a dynamic interface
17
Which of the following IPv6 address prefixes are not routable? (select two)
- FF02::/16
- FE80::/10
- FD00::/8
- FC00::/8
- FF05::/16
- 2000::/3
18
You have been asked to summarize your network addresses into a single summarized subnet. The addresses on your network consist of the following addresses:
10.1.1.64/27
10.1.1.96/27
10.1.1.128/27
10.1.1.160/27
In order to preserve address space, you should summarize these networks by using the most efficient subnet mask
10.1.1.64/27
10.1.1.96/27
10.1.1.128/27
10.1.1.160/27
In order to preserve address space, you should summarize these networks by using the most efficient subnet mask
- /24
- /23
- /25
- /26
19
You have been asked to summarize your network addresses into a single summarized subnet. The addresses on your network consist of the following addresses:
10.1.1.128/27
10.1.1.160/27
10.1.1.192/27
10.1.1.224/27
In order to preserve address space, you should summarize these networks by using the most efficient subnet mask.
10.1.1.128/27
10.1.1.160/27
10.1.1.192/27
10.1.1.224/27
In order to preserve address space, you should summarize these networks by using the most efficient subnet mask.
- /25
- /24
- /23
- /26
20
Which of the following are used by WPA2 to provide MICs and encryption? (Select 2 choices.)
- AES
- CCMP
- TKIP
- RC4
- GCMP
21
You are configuring Layer 2 security on a WLAN by using the WLC GUI. You select WPA+WPA2 from the Layer 2 Security drop-down list box. You want to configure the WPA2 key in hexadecimal format.
Which of the following WPA2 key management methods should you select from the Auth Key Mgmt drop-down list box?
Which of the following WPA2 key management methods should you select from the Auth Key Mgmt drop-down list box?
- PSK
- CCKM
- 802.1X
- 802.1X+CCKM
22
You issue the show vlan brief command on Switch1 and receive the following partial output:
You issue the following commands on Switch1:
Which of the following statements is true? (Select the best answer.)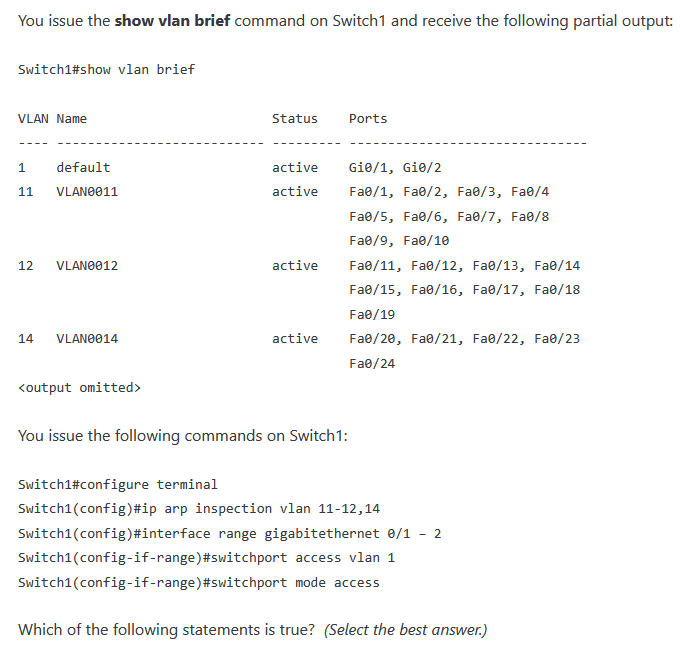
You issue the following commands on Switch1:
Which of the following statements is true? (Select the best answer.)
- DAI is not configured on GigabitEthernet 0/1 and GigabitEthernet 0/2
- Only GigabitEthernet 0/1 and GigabitEthernet 0/2 ports are untrusted ports
- Only GigabitEthernet 0/1 and GigabitEthernet 0/2 are trusted ports.
- DAI is configured on only GigabitEthernet 0/1 and GigabitEthernet 0/2.
23
You are implementing common Layer 2 security measures on a Cisco switch. You create a new VLAN with an ID of 4. No devices operate on VLAN 4. You issue the following commands on a switch interface:
switchport access vlan 4
switchport mode access
Which of the following Layer 2 security measures are you implementing? (Select 2 choices.)
switchport access vlan 4
switchport mode access
Which of the following Layer 2 security measures are you implementing? (Select 2 choices.)
- configuring the port mode manually
- moving the port to an unused VLAN
- enabling port security on an access port
- disabling DTP on a port completely
- disabling an unused port
24
Your company has added an email server and a web server to the existing network infrastructure. Company policy stipulates that only inbound SMTP traffic be allowed to pass to Email Server and that only inbound web traffic be allowed to pass to Web Server. All other traffic must be prevented from reaching the subnet.
Which access lists should be applied to the S0/0 interface of Router1? (Select 2)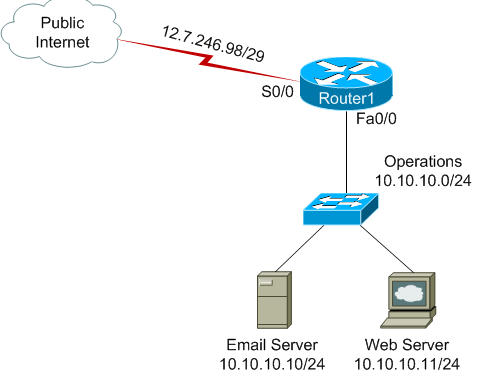
Which access lists should be applied to the S0/0 interface of Router1? (Select 2)
- access-list 101 permit tcp any 10.10.10.11 0.0.0.0 eq 80
- access-list 101 permit tcp any 10.10.10.10 0.0.0.0 eq 25
- access-list 101 permit udp any 10.10.10.11 0.0.0.0 eq 80
- access-list 101 permit udp any 10.10.10.10 0.0.0.0 eq 25
- access-list 101 permit tcp any 10.10.10.10 0.0.0.255 eq 25
- access-list 101 permit tcp any 10.10.10.11 0.0.0.255 eq 80
25
The sending device on a site-to-site VPN that is constructed by using GRE with IPSec for transport encrypts a new packet.
Which of the following steps occurs next? (Select the best answer.)
Which of the following steps occurs next? (Select the best answer.)
- The sending device adds a VPN header and an IP header.
- The sending device adds the session key to the packet.
- The sending device sends the packet to the destination.
- The receiving device decrypts the packet.
26
The sending device on a site-to-site VPN that is constructed by using GRE with IPSec for transport encrypts a new packet.
- The sending device adds a VPN header and an IP header.
- The sending device adds the session key to the packet.
- The sending device sends the packet to the destination.
- The receiving device decrypts the packet.
27
Which of the following entries from the show ip route command indicates a host route?
- L 192.168.1.1/32 is directly connected, FastEthernet0/0
- S* 0.0.0.0/0 [1/0] via FastEthernet0/0
- O 192.168.1.0/24 [110/2] via 10.1.1.13, 00:00:08, FastEthernet0/0
- C 192.168.1.0/30 is directly connected, FastEthernet0/0
- S 192.168.1.0/24 [5/0] via 10.1.2.3
28
You issue the show ip route command on RouterA and receive the following partial output:
S 10.20.0.0/22 [1/0] via 192.168.10.2
R 10.20.0.0/24 [120/3] via 192.168.10.3, 00:33:38, Serial0/3
D 10.20.0.0/26 [90/2809856] via 192.168.10.4, 00:02:14, Serial0/4
O 10.20.0.0/28 [110/64] via 192.168.10.1, 00:02:38, Serial0/1
S 10.20.0.0/22 [1/0] via 192.168.10.2
R 10.20.0.0/24 [120/3] via 192.168.10.3, 00:33:38, Serial0/3
D 10.20.0.0/26 [90/2809856] via 192.168.10.4, 00:02:14, Serial0/4
O 10.20.0.0/28 [110/64] via 192.168.10.1, 00:02:38, Serial0/1
- the OSPF route, because it is the route with the longest prefix match
- the EIGRP route, because it has the lowest AD
- the static route, because static routes are preferred over dynamic routes
- the RIP route, because it has the highest AD
29
You have connected the GigabitEthernet 0/1 interface of RouterC to RouterB and configured the appropriate interface addresses on both routers.
Which of the following commands could you issue on RouterC to enable communication between RouterC and RouterA? (Select all that apply.)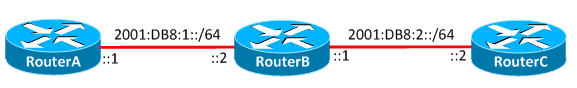
Which of the following commands could you issue on RouterC to enable communication between RouterC and RouterA? (Select all that apply.)
- ipv6 route ::/0 GigabitEthernet 0/1
- ipv6 route 2001:DB8:1::/64 2001:DB8:2::1
- ipv6 route 2001:DB8:2::/64 2001:DB8:1::2
- ipv6 route 2001:DB8:2::1 2001:DB8:1::/64
- ipv6 route 2001:DB8:1::2 2001:DB8:2::/64
30
You issue the following commands on a Cisco router's FastEthernet 0/0 interface:
ipv6 address 2001:DB8:A::/64 eui-64
no shutdown
The interface on the other side of the link is not yet configured. In addition, there is no DHCPv6 server on the network.
ipv6 address 2001:DB8:A::/64 eui-64
no shutdown
The interface on the other side of the link is not yet configured. In addition, there is no DHCPv6 server on the network.
- two
- one
- none
- three
31
Which of the following statements is true regarding the ip access-group command?
- It can be used to apply an ACL to an IPv4 interface
- It can be used to apply an IPv4 ACL to a vty line
- It can be used to apply an ACL to an IPv6 interface
- It can be used to apply an IPv6 ACL to the AUX line
32
Which wireless security protocol relies on SAE and introduces support for PMF?
- WPA3-Personal
- WPA2-Personal
- WPA3-Enterprise
- WPA2-Enterprise
33
Which of the following commands should you issue in order to encrypt the password that is required to access privilege level 7 on a router?
- enable secret level 7 cisco
- enable secret 7 cisco
- enable password 7 cisco
- enable password level 7 cisco
34
You are configuring Layer 2 security on a WLAN by using the WLC GUI. You select WPA+WPA2 from the Layer 2 Security drop-down list box. You then select the MAC Filtering option to ensure that only specific clients can join, and you select the WPA2 Policy option to ensure that WPA2 is used. You want to minimize the amount of time it takes an 802.1X client to roam between APs.
Which of the following WPA2 key management methods should you select from the Auth Key Mgmt drop-down list box?
Which of the following WPA2 key management methods should you select from the Auth Key Mgmt drop-down list box?
- 802.1X+CCKM
- CCKM
- PSK
- 802.1X
35
Which of the following statements are true about IPSec configured in tunnel mode? (Select 2)
- It is often used in networks with private IP addresses
- It encrypts both the IP header and the payload
- It encrypts the payload but does not encrypt the IP header
- It encrypts the IP header but does not encrypt the payload
- It is less secure than IPSec configured in transport mode
36
You issue the following commands on Switch1:
Switch1(config)#ip arp inspection vlan 11,14,18
Switch1(config)#interface fastethernet 0/1
Switch1(config-if)#switchport access vlan 14
Switch1(config-if)#switchport mode access
Switch1(config-if)#ip arp inspection trust
Switch1(config-if)#interface range fastethernet 0/2 - 4
Switch1(config-if-range)#switchport access vlan 14
Switch1(config-if-range)#switchport mode access
Which of the following statements are true? (Select 2 choices.)
- The FastEthernet 0/1 port in VLAN 14 is a trusted port
- Every port except the FastEthernet 0/1 port in VLAN 14 is an untrusted port
- Ports in every VLAN except VLAN 14 are trusted ports
- Every port in VLANs 11, 14, and 18 is an untrusted port
- All ports in VLAN 14 are trusted ports
37
You issue the following command on a Cisco router in global configuration mode:
ipv6 route 2001:db8:a::/32 fastethernet 0/1
Which of the following have you created?
ipv6 route 2001:db8:a::/32 fastethernet 0/1
Which of the following have you created?
- a directly attached static route
- a recursive static route
- a fully specified static route
- a floating static route
38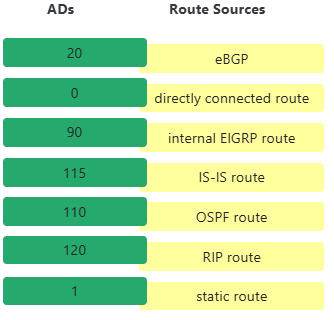
Select the following ADs, and drag them to their corresponding route sources. 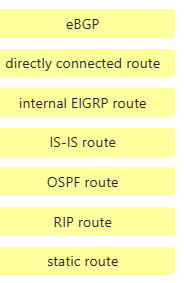
39
You issue the ip ospf network non-broadcast command on an interface.
Which of the following statements is correct regarding how OSPF operates on the interface? (Select the best answer.)
Which of the following statements is correct regarding how OSPF operates on the interface? (Select the best answer.)
- The neighbor command is required to establish adjacencies.
- DR and BDR elections are not performed.
- The hello timer is set to 10 seconds, and the dead timer is set to 40 seconds.
- Multicast updates are sent.
40
How is the OSPF DR for a multiaccess network segment determined?
- first by the highest OSPF priority value, then by the highest configured router ID, then by the highest loopback IP address, and then by the highest physical IP address
- first by the highest OSPF priority value, then by the highest loopback IP address, and then by the highest physical IP address
- first by the highest configured router ID, then by the highest OSPF priority value, then by the highest loopback IP address, and then by the highest physical MAC address
- first by the highest router ID, then by the highest loopback IP address, and then by the highest physical IP address
- first by the highest router ID, then by the highest loopback IP address, and then by the highest physical MAC address
- first by the highest OSPF priority value, then by the highest router ID, and then by the highest IP address
41
Your supervisor wants you to reduce the range of IP addresses available from a NAT pool that is configured on the department router. You should do this by enabling internal hosts to share a single external IP address.
Which of the following should you configure on RouterA?
Which of the following should you configure on RouterA?
- NAT overloading
- dynamic NAT
- NAT overlapping
- static NAT
42
Which of the following can be implemented to help protect against spoofed management frames in a wireless network?
- 802.11v
- 802.11k
- 802.11w
- 802.11r
43
Which of the following statements is accurate regarding alternate ports?
- An alternate port is a blocked port that receives more useful BPDUs from a port on another switch
- An alternate port is always in the forwarding state
- An alternate port is a blocked port that receives more useful BPDUs from another port on the local switch
- An alternate port is the port on a switch that has the best path to the root bridge
- An alternate port is the port on a segment that has the best path to the root bridge
44
Which of the following subnet addresses is most appropriate for the point-to-point link between RouterA and RouterB?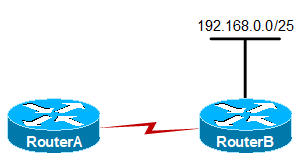
- 192.168.0.128/25
- 192.168.0.128/30
- 192.168.0.0/30
- 192.168.0.130/30
- 192.168.0.0/25
- 192.168.0.192/26
45
Which of the following digital networking technologies has a total bandwidth of 1.544 Mbps? (Select the best answer.)
- T1
- T3
- E1
- E3
46
Which of the following are used by WPA2 to provide MICs and encryption? (Select 2 choices.)
- AES
- CCMP
- TKIP
- GCMP
- RC4
47
You administer the network shown above. You want to configure RouterA so that only RouterB can Telnet to RouterA. No other traffic to or from RouterA should be affected.
Which of the following commands should you issue to complete this task? (Select all that apply.)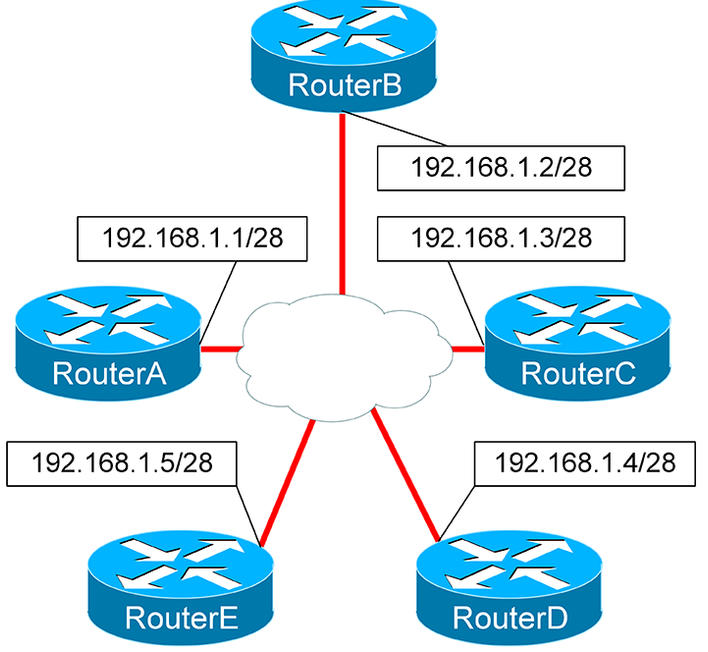
Which of the following commands should you issue to complete this task? (Select all that apply.)
- access-list 10 permit 192.168.1.2 0.0.0.15
- ip access-group 10 in
- ip access-group 10 out
- access-class 10 in
- access-class 10 out
- access-list 10 permit 192.168.1.2 0.0.0.0
48
Which of the following technologies is implemented in WPA3-Enterprise to improve authentication encryption?
- AES-GCMP
- ECDSA
- SAE
- PMF